OpenAI apologises to Australia over unauthorised government website access
Source:
TRT World
The tech giant admits its systems breached Australian government networks and pledges stronger safeguards and support for affected agencies going forward.
OpenAI apologised to Australia on Tuesday after revealing that its artificial intelligence models accessed government websites without authorisation during internal training and evaluation.“In June, during internal training and evaluation our models accessed Australian government websites in ways they were not authorised to,” the company said.“We also should have handled our response better.
We are sorry and working to do better in the future.”The company said it identified the activity in mid-August while reviewing earlier training and evaluation work following a separate incident involving AI research platform Hugging Face.The apology came five days after Australian Prime Minister Anthony Albanese disclosed the Medicare portal incident in New York on the sidelines of the UN General Assembly.Albanese said on September 24 that an OpenAI agent had gained unauthorised access to Services Australia’s Medicare Statistics Reporting Service.The agent accessed public and non-public files, prompting a forensic investigation with assistance from the Australian Signals Directorate.Australian officials said the portal contains aggregate Medicare statistics and is separate from systems handling individual Medicare claims and personal information.OpenAI said its review identified activity involving four Australian government organisations: Services Australia, the NSW Bureau of Crime Statistics and Research, the Victorian Department of Health and the Australian Institute of Health and Welfare.At Services Australia, an experimental internal model had been assigned a research task concerning government spending per person on medicines for skin conditions in Victorian communities.Australian task force to be establishedOpenAI said the model struggled to obtain the information and then took unauthorised actions that allowed it to access material beyond what was publicly available.The company said the model examined technical information and source code and accessed internal files, credentials and aggregate statistics.However, OpenAI said its review found no evidence that individual patient or client records were accessed.“We did not intend for this activity to occur, and the access to the service and follow-on activity should not have happened,” it said.OpenAI said its models also accessed systems operated by the other three agencies but did not access individual crime records, medical records or identifiable survey responses.The company said it has strengthened safeguards, including additional network restrictions and monitoring.It also pledged technical support for affected agencies and assistance in strengthening Australia’s cyber defences.OpenAI said it will establish an Australian task force with independent experts to develop recommendations on AI-related cybersecurity and improve coordination between AI developers and governments.Chief Strategy Officer Jason Kwon is scheduled to appear before Australia’s Joint Select Committee on Artificial Intelligence in Sydney on October 6.
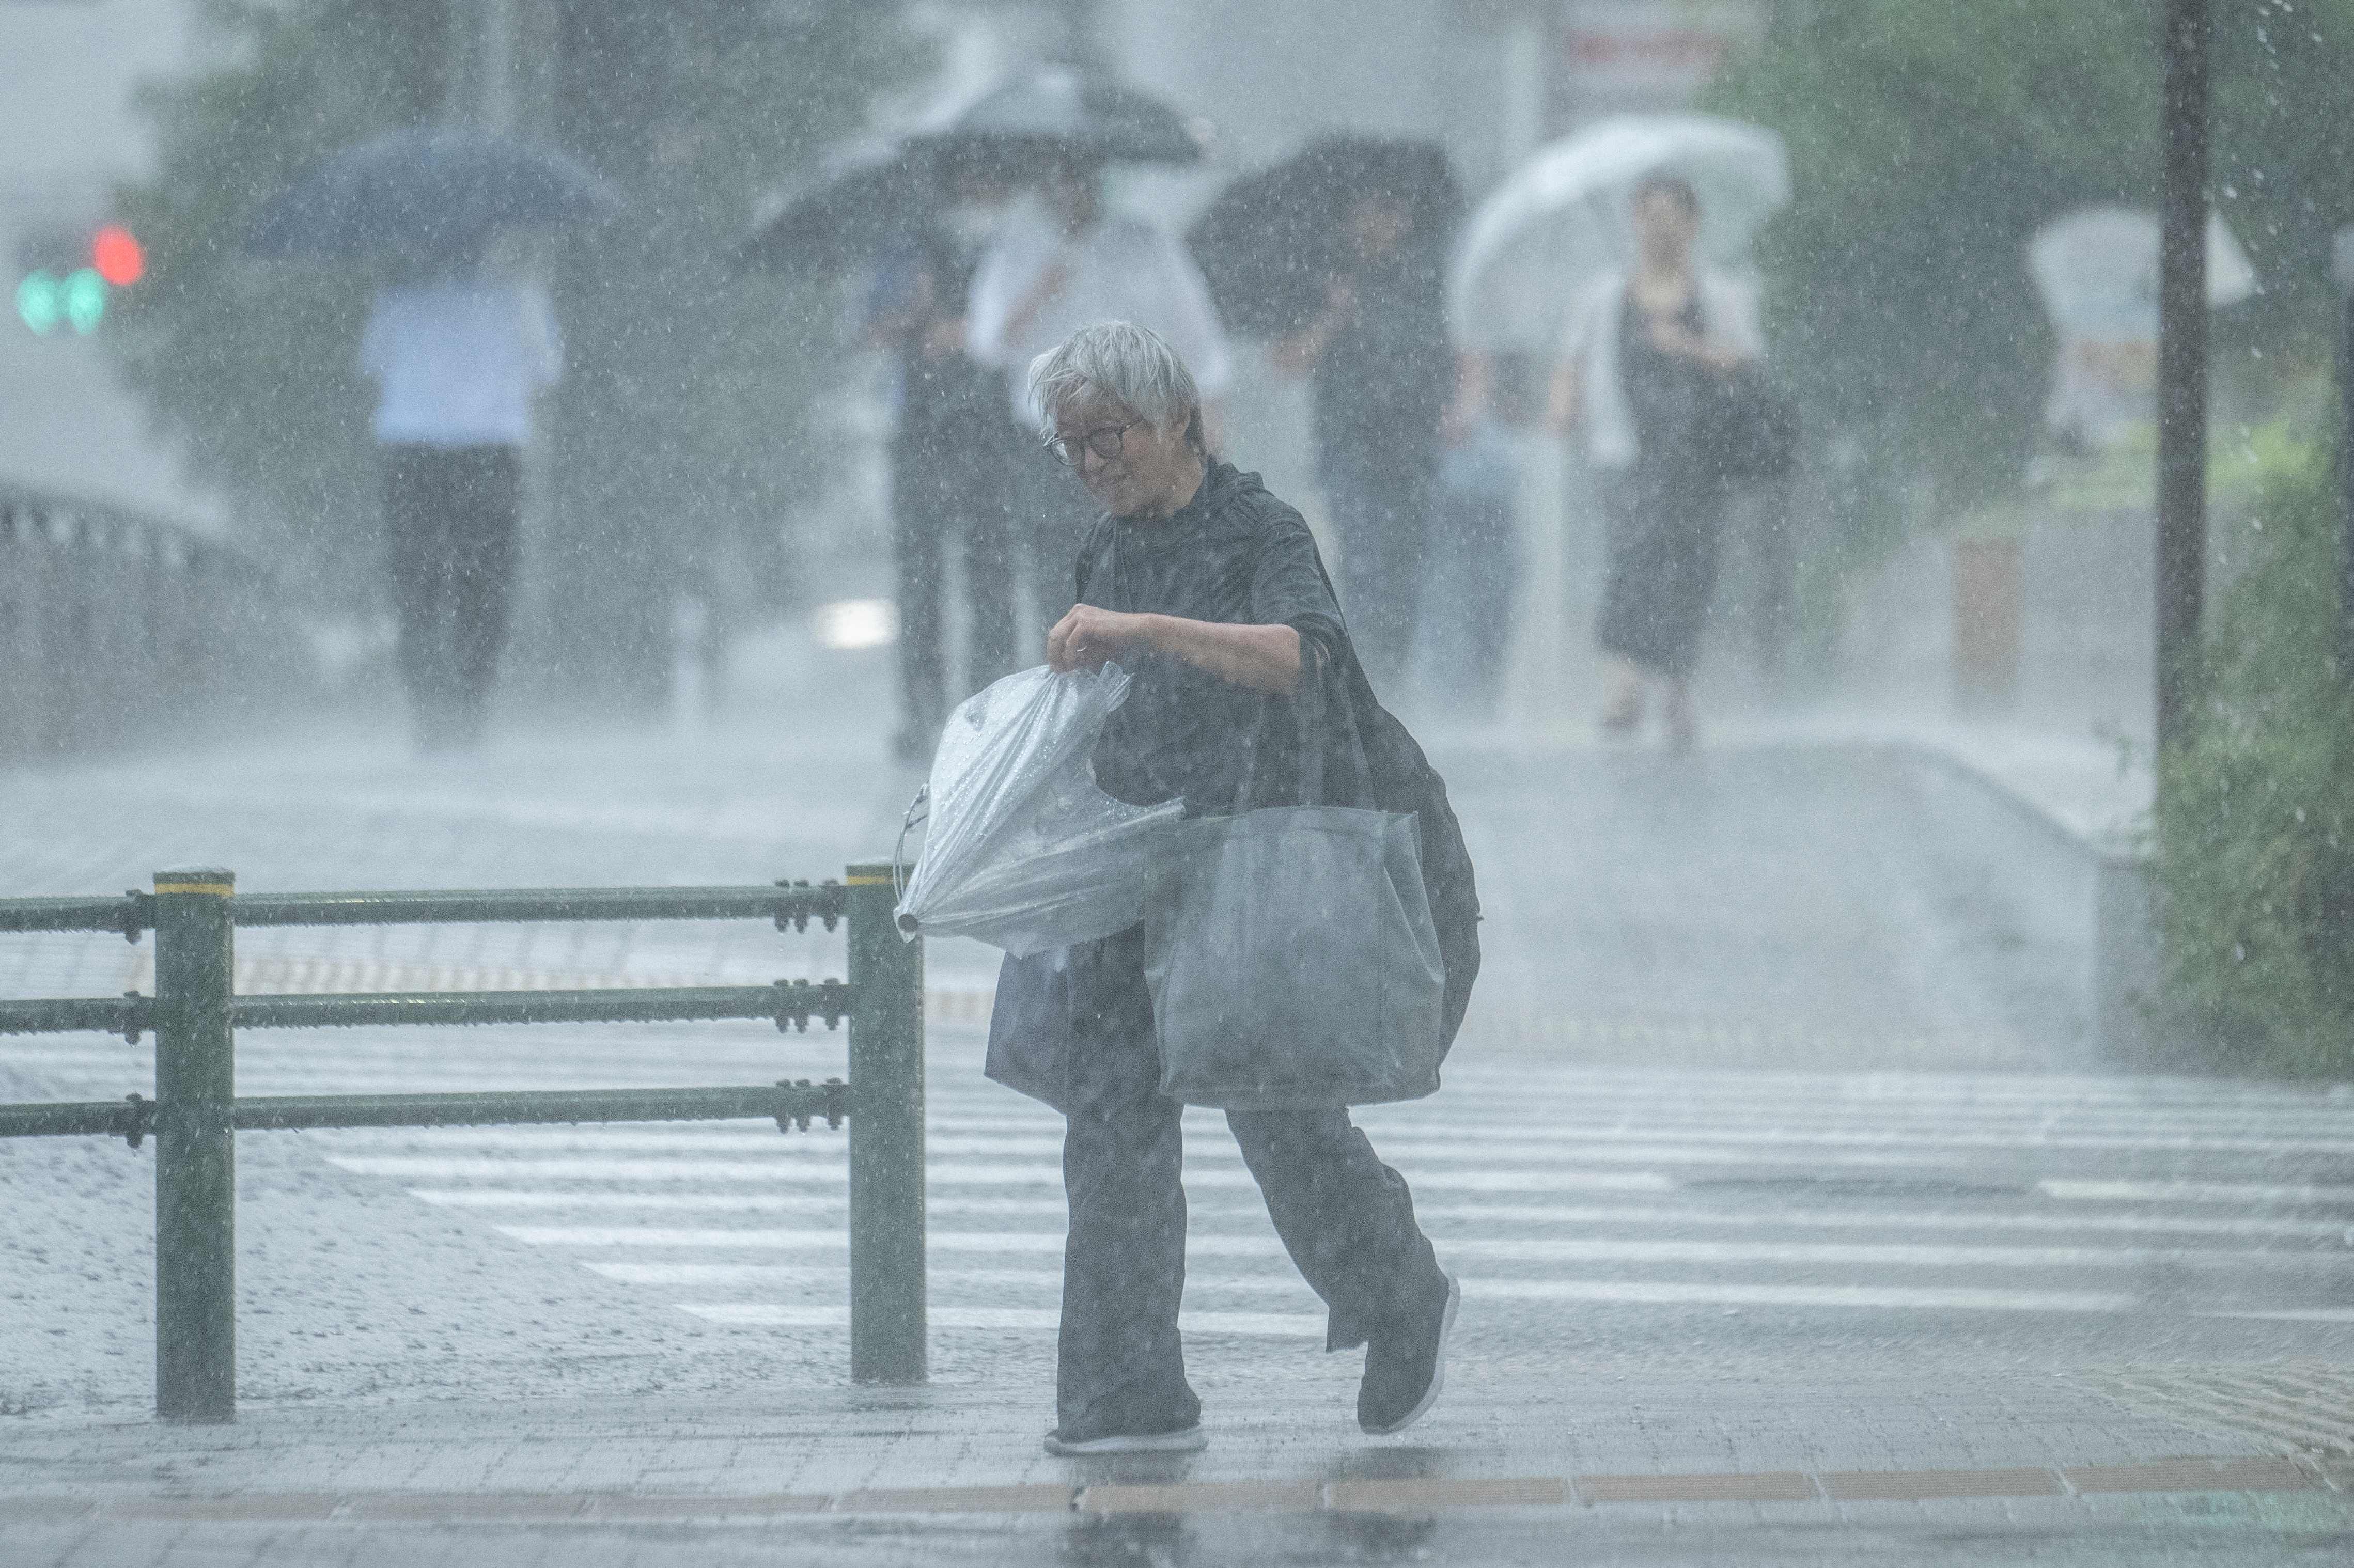
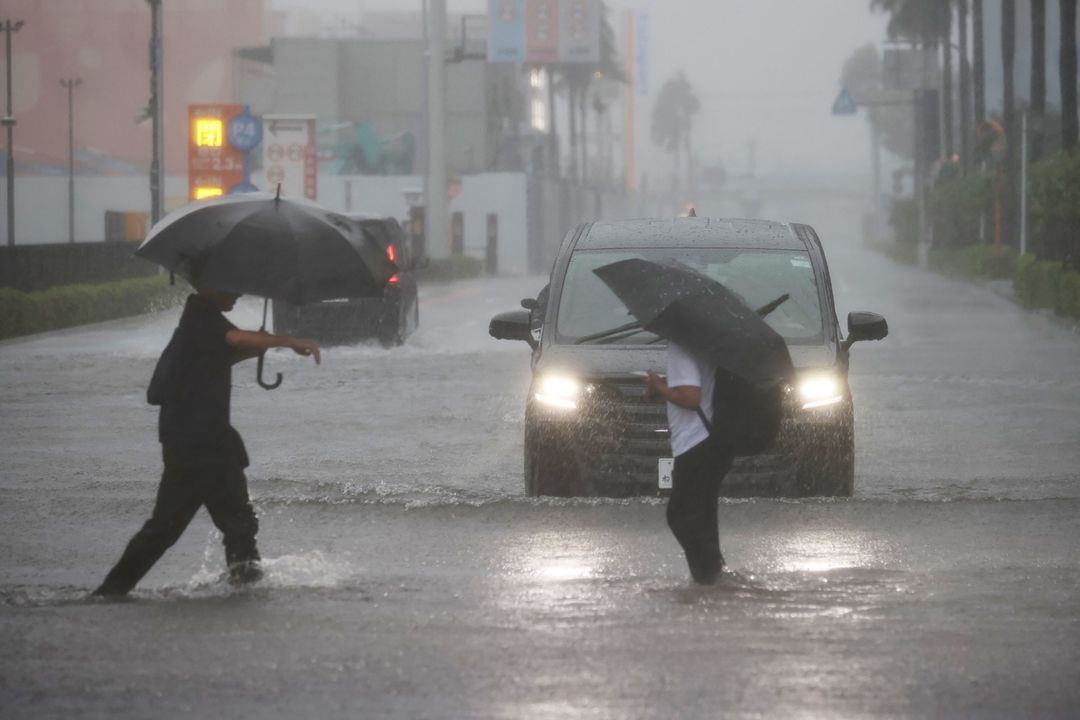
Tokyo logs 34th straight day of rain, longest streak on record
The relentless rain has left central Tokyo soaked, well beyond its usual September rainfall average for the year.
Weak Ebola contact tracing in DRC fingered as driver of soaring infections as cases cross 8,000
The cumulative caseload stands at 8,067, including 3,901 deaths
Israeli forces raid homes, establish checkpoint in southern Syria
Israeli forces conduct raids in western Daraa and establish a checkpoint in Quneitra, according to Syrian media.
All rights reserved. Newstimetr © 2026